Node.js 41 🟢 Preventing SQL Injection with Parameterized Queries
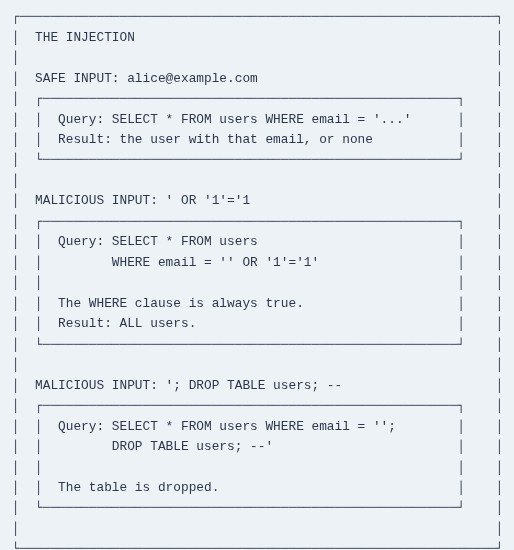
SQL injection is the most persistent vulnerability in web applications. It has been in the OWASP Top 10 since the list was created, and it remains there because the underlying mistake is so easy to make. The mistake is string concatenation: building a query by pasting user input into a template. The input is treated…