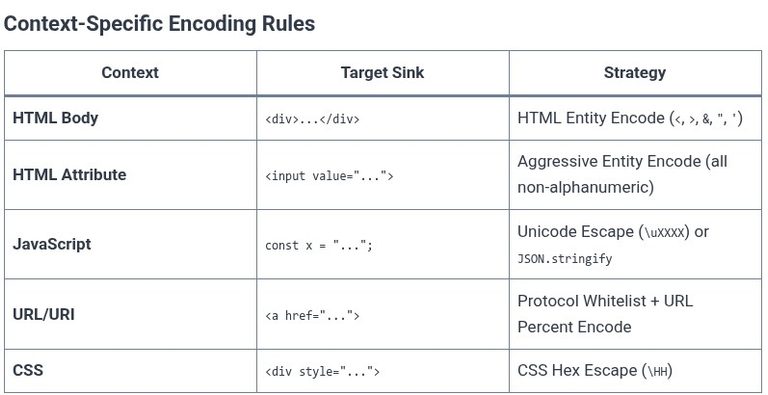
Web Security 05 🛡️ Context-Aware Encoding & Sanitization — Safe DOM rendering, framework escapes, and DOMPurify implementation
In the landscape of web security, “Sanitization” and “Encoding” are the primary defensive countermeasures against Cross-Site Scripting (XSS). While input validation attempts to ensure data conforms to a specific format before it enters a system, encoding and sanitization focus on the output—ensuring that when data is eventually rendered in a browser, it is interpreted strictly…