GitHub 21 🌐 GitHub Secret Scanning and CodeQL Analysis
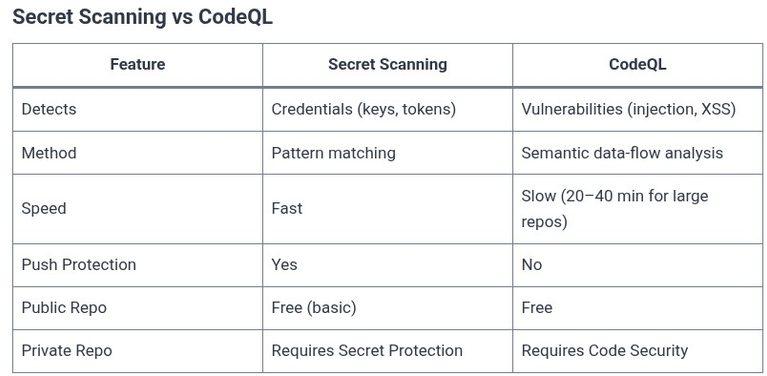
GitHub provides two distinct static analysis security features: Secret Scanning, which detects leaked credentials in code and text, and CodeQL Analysis, which performs semantic code analysis to find vulnerabilities like SQL injection or cross-site scripting. A critical change occurred in May 2025: CodeQL no longer detects hardcoded secrets. Secret Scanning is now the sole mechanism…