Programming | Docker | Tools
Docker 54 🐳 Restricting System Calls: Custom Seccomp Profiles in Docker Engine
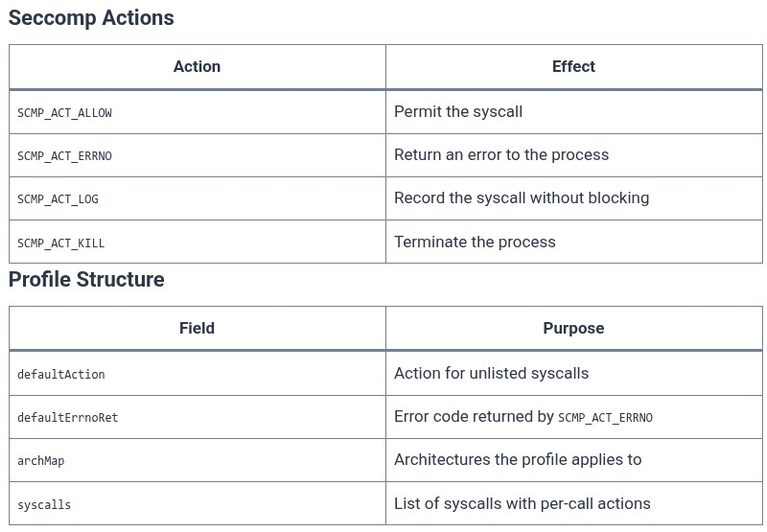
A container shares the host kernel. Every action the containerized process takes, from opening a file to sending a network packet, is a system call into that kernel. The kernel’s syscall interface is the largest attack surface in the container model: roughly 300 calls, each a potential entry point for a kernel vulnerability. Seccomp (secure…