Docker 93 🐳 Kernel Resource Auditing: Tracing System Calls inside Containers using strace and eBPF
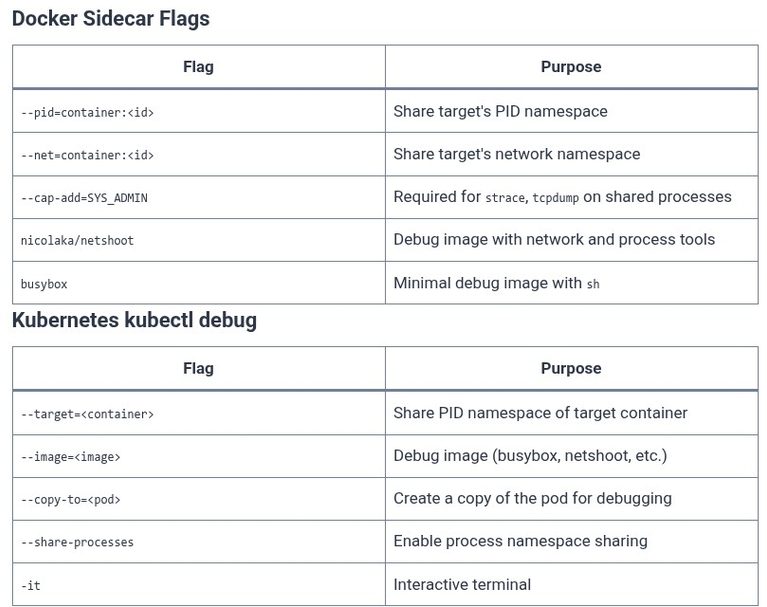
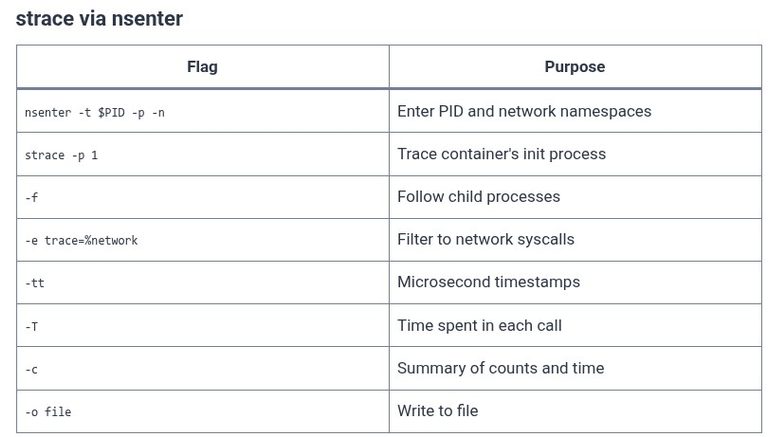
Container system call tracing is complicated by two facts that are easy to overlook. First, minimal container images—the ones most likely to be deployed in production—often exclude strace and other debugging tools precisely because they increase the attack surface . Second, strace relies on the ptrace system call, which requires the CAP_SYS_PTRACE capability that Docker…