Docker 29 🐳 Read-Only Containers (–read-only) and Mounting Temporary In-Memory File Systems
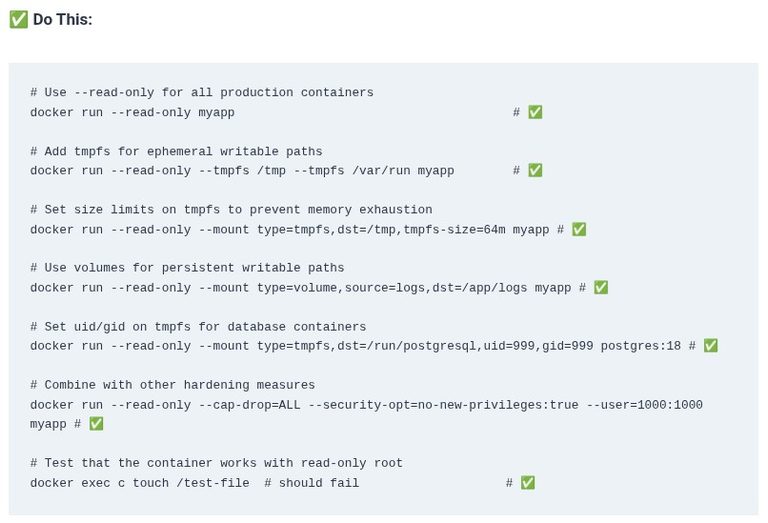
A container’s root filesystem is writable by default. The application can write to any directory that its user has permission to write to, including the directories where the application’s own binaries and configuration files live. This is convenient for development and for applications that assume they can write anywhere. It is also a security liability….